ONUS
Security findings are only useful when you know what to do next.
I designed ONUS as a supervised project during my IIT Kanpur Computer Centre internship, then released it as open source. Eight parallel scanning modules feed a normalized finding schema in a self-hosted, air-gap capable platform. A passive re-observation step assigns confirmed, probable, or unverified confidence, while AI-generated remediation prose stays separate from scoring. I deployed it on Oracle Cloud ARM64 behind Caddy and TLS; it is listed in OWASP’s Vulnerability Scanning Tools directory.
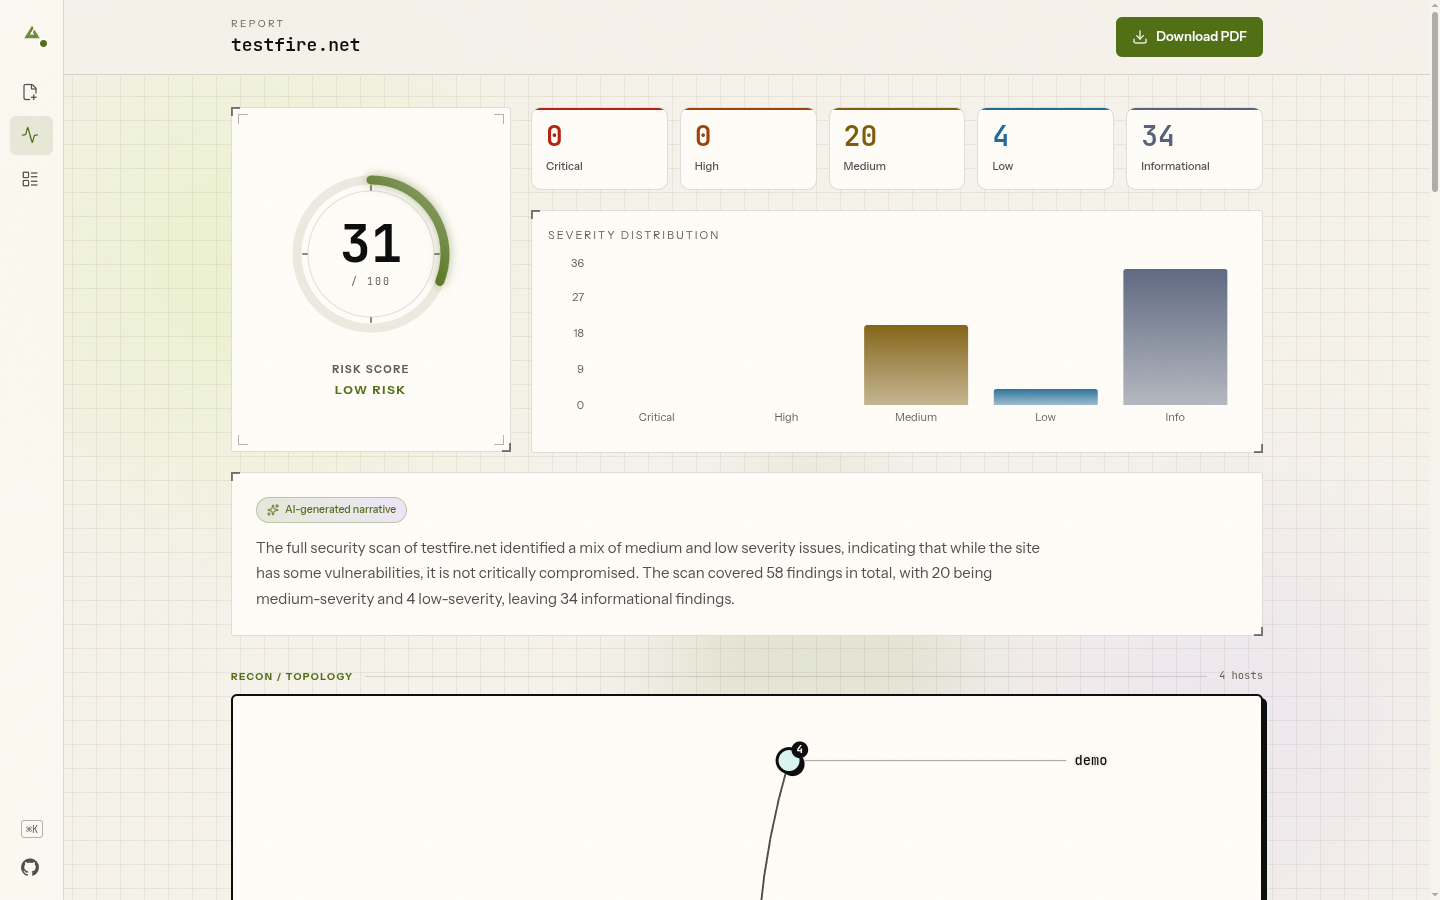
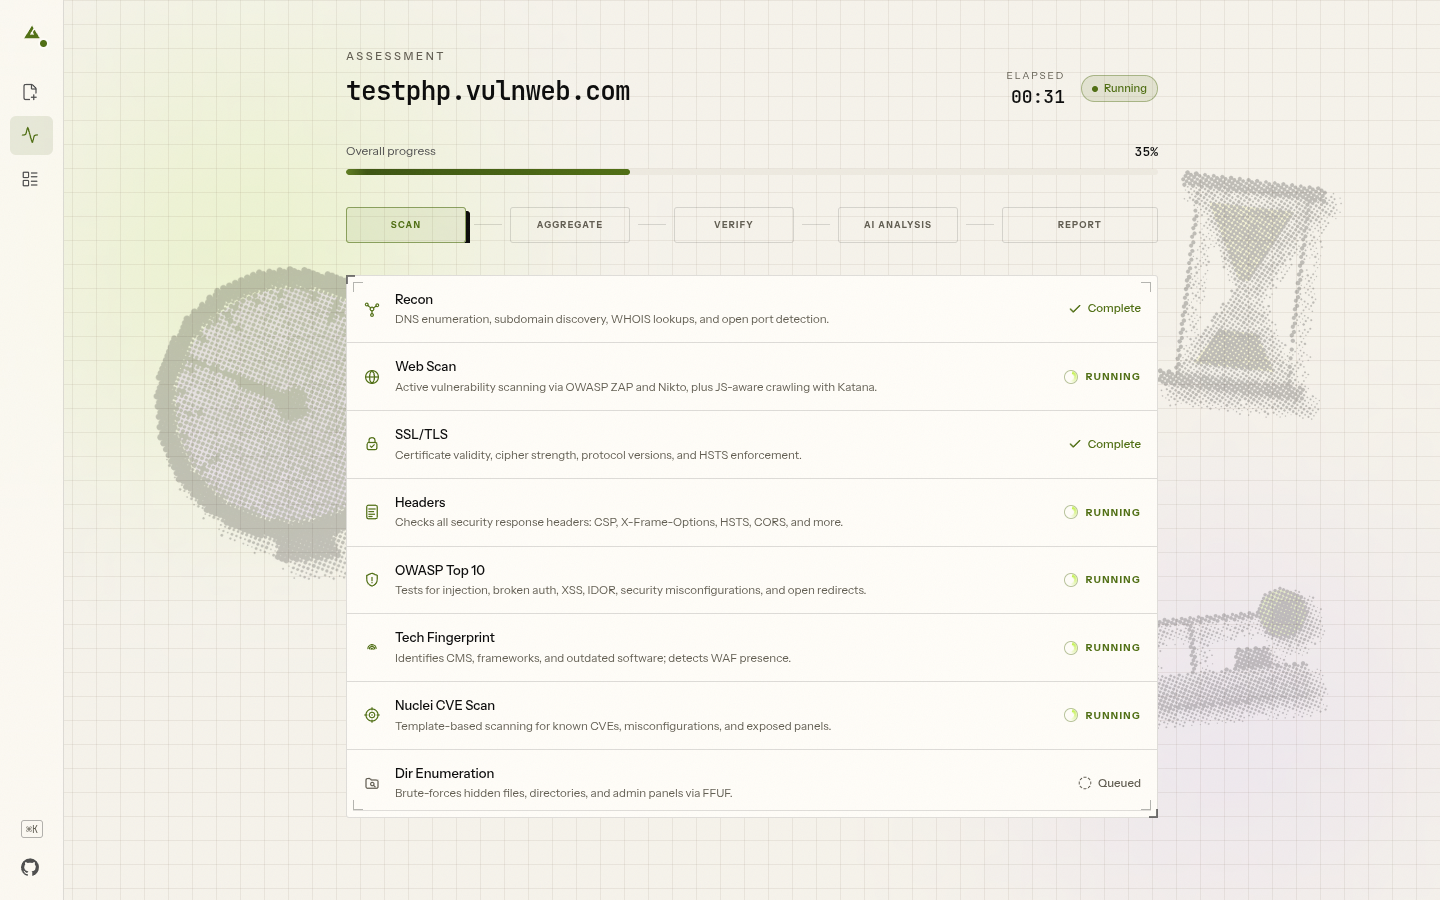
Eight tools, one evidence trail.
Nmap, ZAP, Nikto, Nuclei, testssl.sh, FFUF and other modules produce findings that ONUS normalizes into a single schema. Each result keeps its evidence and confidence state visible.
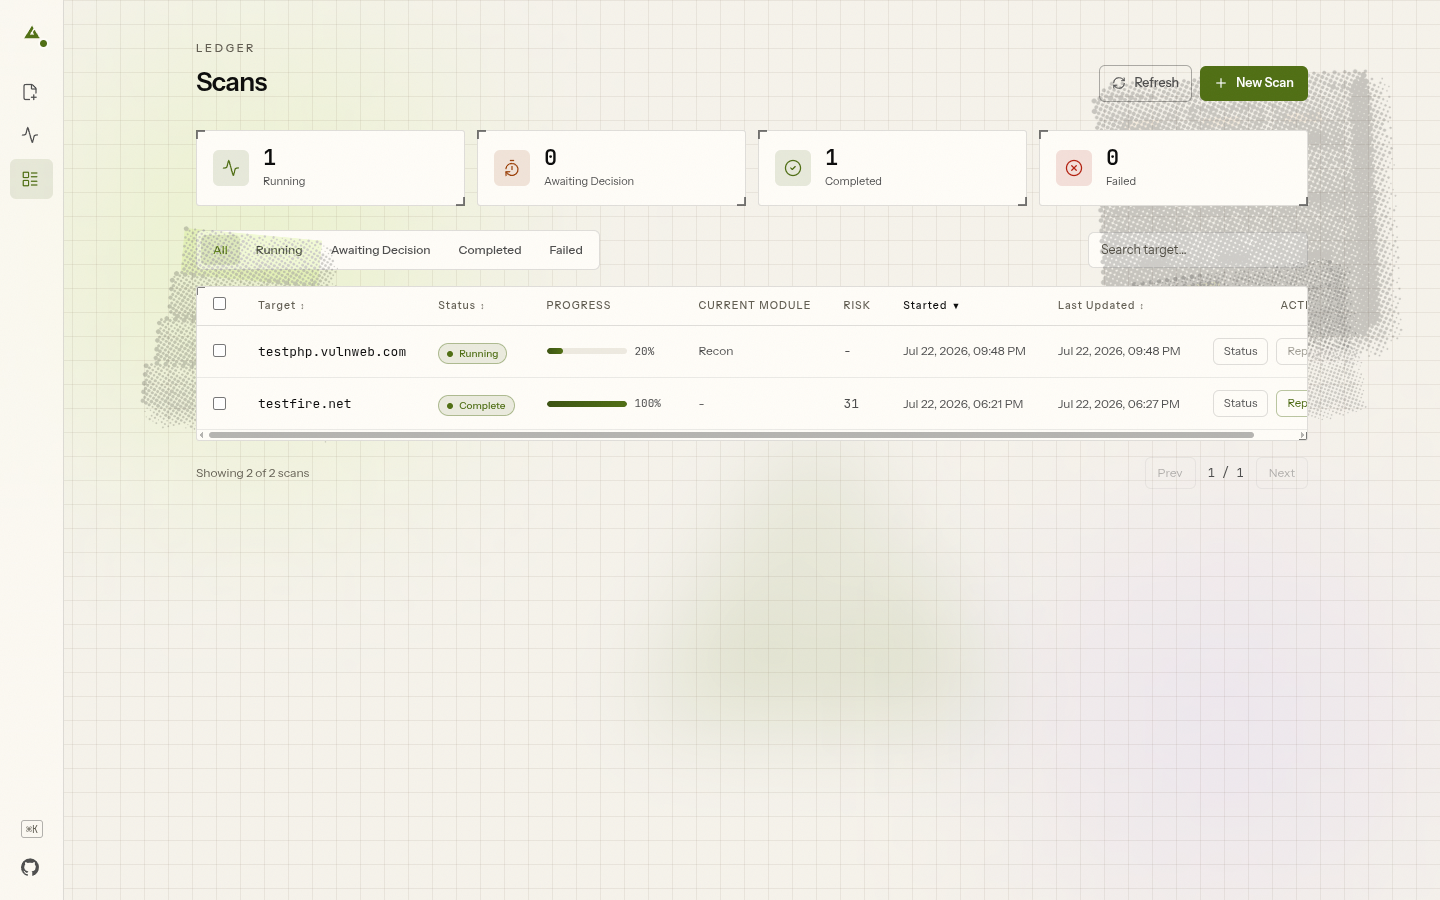
The score is deterministic.
A CVSS v3.1 engine covers 73 finding types. Across 690 pytest tests, repeat scans produce byte-identical scores. AI explains remediation but never changes the score.
A deployable, inspectable system.
The platform can run self-hosted or air-gapped. I migrated a deployment to Oracle Cloud ARM64 with a hardened Caddy reverse proxy and TLS, and published the source at github.com/maverickaayush/ONUS.